EXCEED CyberSecurity
Sample environment Back to site Schedule a call
Demo dashboard

See what your assessment looks like.

A fictional engagement against a sample enterprise platform. Every target, finding and timestamp below is synthetic.

Demo only. The credentials testuser / mytestuserpass are intentionally published here and protect nothing. No real assessment data exists behind this page.
Exceed CyberSecurity / Engagement EX-2026-0147

Northwind Group: Platform & API Assessment

Target app.northwind••••.com Scope Web + REST API Tested 18 Sep 2026 Status In remediation Operator M. Kadir
Security posture
68/100
Needs attention
Validated findings
5
1 critical, 2 high, 1 medium, 1 low
Attack surface
214
Hosts and API routes analysed
Discarded at gate
31
Candidates with no reachable impact
Time to report
9h 42m
Agentic testing plus operator review

Executive summary

Agentic assessment with offensive-security operator review

The platform presents a moderate security risk driven primarily by authorisation weaknesses in the API layer. The most severe finding allows one authenticated tenant to read another tenant's records by editing a predictable object identifier. Two further findings compound it: a privilege escalation on the role-update flow and a stored cross-site scripting issue in shared workspace content. Remediate tenant isolation and the role-update authorisation first, then close the client-side hardening gaps.

Moderate posture

Meaningful controls are in place, but two high-impact authorisation issues should be closed before the next audit window.

Target posture after remediation: 85+

Findings

5 validated
Every entry reproduced by hand before publication
EX-001
Cross-tenant access via API object identifiers
Authorisation API CWE-639 CVSS 7.7
CRITICAL
Impact

Any authenticated user can retrieve records belonging to another organisation by incrementing a predictable resource identifier. Tenant isolation is broken across every customer on the affected path.

Affected area GET /api/v1/••••/records/{id}
Recommended fix: enforce a server-side tenant ownership check on every object access, scope queries by tenant at the data layer, and replace sequential integer identifiers with non-guessable UUIDs.
Operator validated, severity raised from High
EX-002
Privilege escalation through the role update flow
Access control Business logic CWE-269 CVSS 8.1
HIGH
Impact

The server trusts a client-supplied role field when processing a role change, so a member-level account can reach an administrator-only capability within its tenant.

Affected area POST /api/v1/••••/members/role
Recommended fix: resolve the acting principal's role server-side from the session, reject requests carrying a role context, and enforce function-level authorisation in middleware rather than per handler.
Operator validated, chains with EX-001
EX-003
Stored XSS in shared workspace content
Injection Web CWE-79 CVSS 7.3
HIGH
Impact

Markup stored through the API bypasses client-side sanitisation and executes in the authenticated session of any colleague who opens the shared workspace.

Affected area Workspace rich-text editor, customer-supplied content
Recommended fix: sanitise server-side at write time with a strict allowlist, apply contextual output encoding at render, enforce a nonce-based Content-Security-Policy, and sweep historical content.
Operator validated
EX-004
Insufficient rate limiting on authentication
Authentication Abuse prevention CWE-307 CVSS 5.3
MEDIUM
Impact

Throttling is bound to source address rather than to the targeted account, so attempts distributed across addresses avoid lockout.

Affected area POST /auth/login
Recommended fix: add a per-account attempt counter with exponential backoff, challenge after a low failure threshold, extend enforced MFA to all users, and alert on distributed authentication failure.
Operator validated, downgraded from High (WAF policy mitigates)
EX-005
Incomplete security header baseline
Hardening Web CWE-693 CVSS 3.1
LOW
Impact

Content-Security-Policy, X-Content-Type-Options, Referrer-Policy and Permissions-Policy are absent, and HSTS max-age is too short. Nothing is exploitable through this alone, but the gaps removed the controls that would have contained EX-003.

Affected area Application response headers
Recommended fix: apply the baseline at the edge, roll CSP out in report-only mode first, and raise HSTS max-age once subdomain coverage is confirmed.
Operator validated

Proven attack path

Chained route from a single low-privilege account to tenant takeover
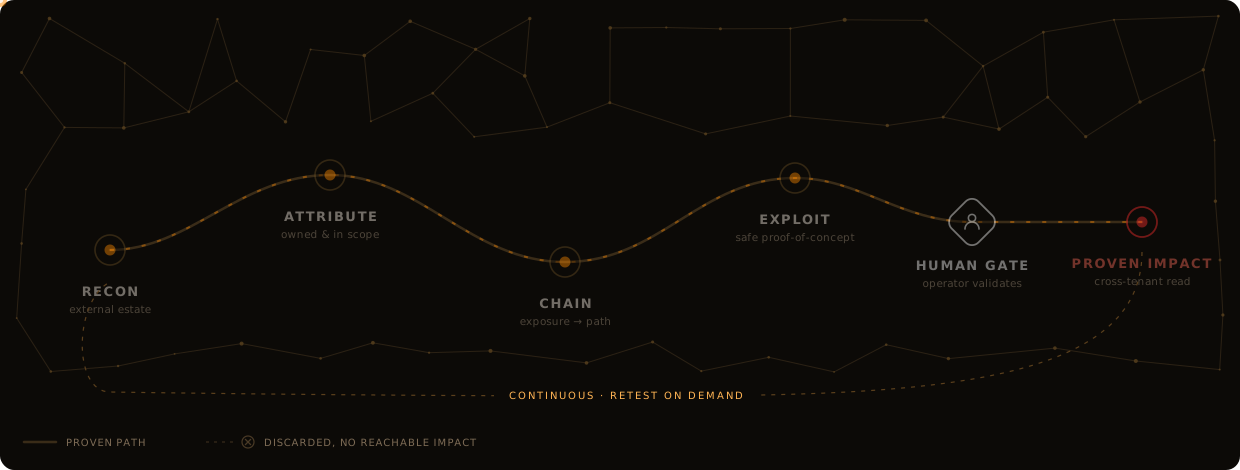
The engagement attack path: reconnaissance, asset attribution, exposure chaining and a safe proof-of-concept, validated by an operator before being reported as proven impact.

EX-001 exposes records across tenants and identifies an administrator. EX-003 delivers a payload into a workspace shared with that administrator. EX-002 elevates a controlled account. Outcome: full administrative control of the target tenant with cross-tenant read retained. Each step was individually validated; the chain was not executed end to end against a live tenant.

Human validation gate

PASSED
What the operator did with the engine's output
36Candidates raised by the agentic phase
5Reproduced and reported
31Discarded, no reachable impact
2Severity adjusted against business context
M. Kadir Lead operator, OSCP / OSCE / OSEP

Severity distribution

Across validated findings only
Critical 1 High 2 Medium 1 Low 1
AuthenticationGood
AuthorisationNeeds work
API securityNeeds work
Input handlingFair
Client-side hardeningFair
InfrastructureGood

Remediation timeline

Suggested order to reach 85+
Day 0-2
Close EX-001Tenant isolation, object authorisation
P0
Day 2-4
Close EX-002Server-side role resolution
P1
Day 4-9
Close EX-003Sanitisation, CSP, content sweep
P1
Week 3
Close EX-004 and EX-005Abuse controls, header baseline
P2
Week 4
Retest and attestationSigned artefact for your assessor
QA

Compliance readiness

Evidence status for the control each framework asks for
SOC 2 Type IICC4.1 / CC7.1
EVIDENCE READY
ISO/IEC 27001:2022A.8.8 / A.8.29
EVIDENCE READY
PCI DSS 4.0Req. 11.4.1 to 11.4.5
PENDING RETEST
NIS2Art. 21(2)
EVIDENCE READY
DORAArt. 24 to 26
SCOPE EXTENSION

Full report

Complete assessment output

The full report adds methodology, rules of engagement, per-finding evidence, reproduction steps, CVSS vectors, cross-cutting analysis and the compliance mapping appendix.

Open the sample report

Illustrative data only. The target, operator, findings, scores and timestamps on this page are fictional or masked for demonstration. No client-identifying information is shown anywhere in this sample, and Exceed does not publish real engagement data without written client permission.